



 USD

Polymarket Resumes Trading After Third-Party Exploit Hits Users

Platform says provider was compromised as researchers trace millions in losses
TL;DR
- Polymarket temporarily restricted trading after a compromised third-party provider affected its international platform.
- Arkham identified a suspected attacker wallet holding about $2.65 million in POL after several token swaps.
- Polymarket resumed trading after fixing the issue and said affected traders would be fully reimbursed.
Trade smarter on Jupiter, Solana’s leading DEX built for fast execution and deep liquidity.
Swap tokens at competitive rates, route across multiple liquidity sources automatically, and access perpetuals, DCA, and advanced trading tools — all in one place!
Polymarket resumed trading on Oct. 29 after a third-party provider was compromised in an exploit that caused user losses on its international platform. The prediction market temporarily stopped normal trading and relayer activity while investigating, then said it had found and fixed the cause and would fully reimburse affected traders.
Polymarket first said at 2:33 p.m. ET that it had identified an issue affecting Polymarket.com and paused trading as a precaution. During the investigation, the exchange entered cancel-only mode, allowing existing orders to be canceled while preventing new orders and trades from processing. Relayer actions were also paused.
“We're still looking into this,” the platform said. “The exchange is in cancel-only mode. You can cancel orders, but no new orders or trades are processing. Relayer actions are paused while we investigate.”
Third-party provider identified as source of incident
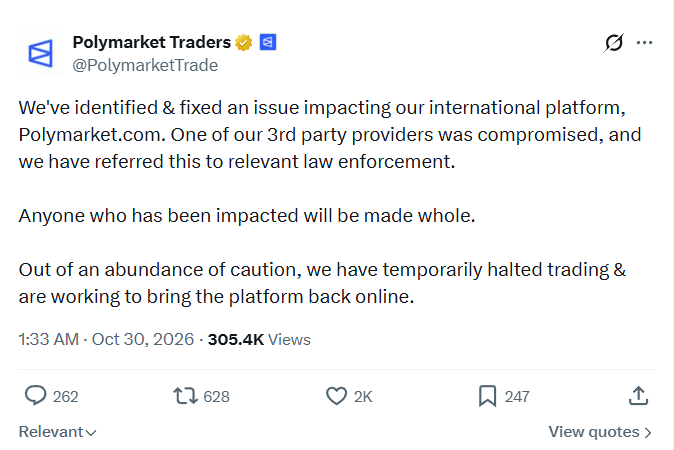
Polymarket later said it had “found the cause” and fixed the issue. The company attributed the incident to a compromised outside service and said law enforcement had been contacted.
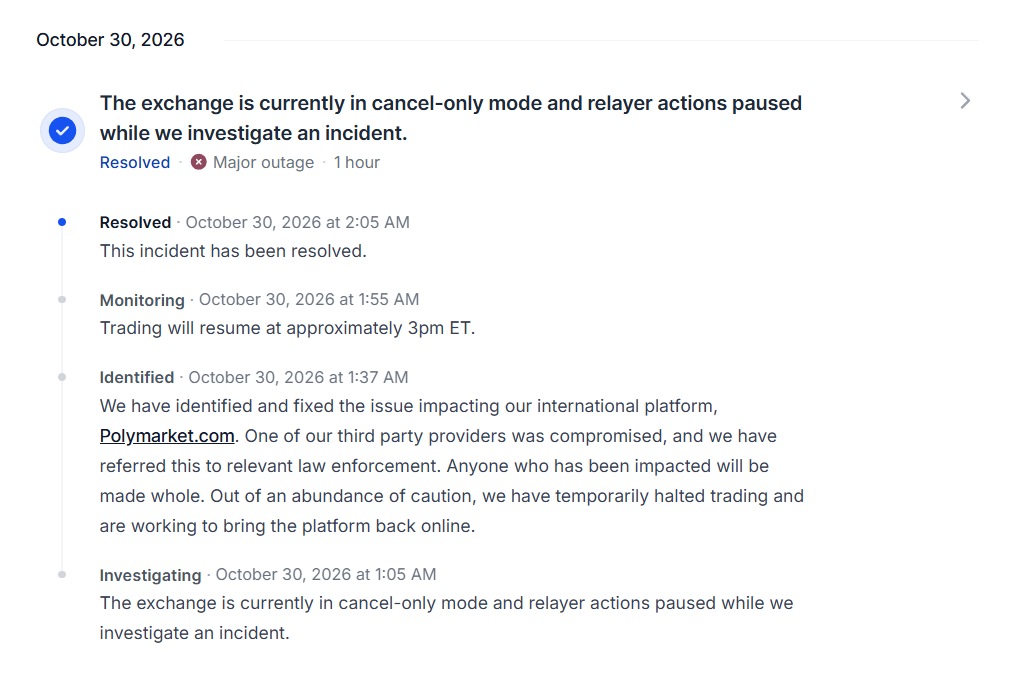
“We’ve identified and fixed an issue impacting our international platform. One of our third-party providers was compromised, and we have referred this to relevant law enforcement,” Polymarket said. “Anyone who has been impacted will be made whole.”
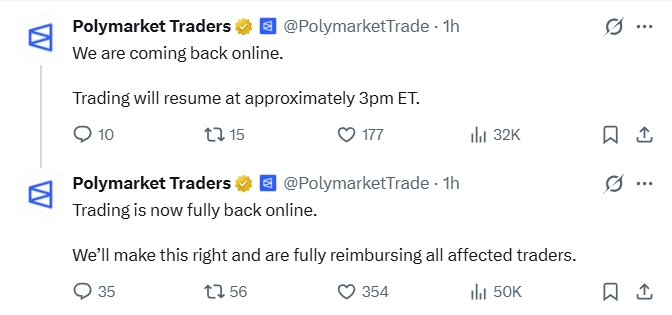
Trading resumed at approximately 3:00 p.m. ET. Polymarket subsequently said, “we’ll make this right and are fully reimbursing all affected traders.”
0xngmi, the pseudonymous developer behind DeFi analytics resource DeFiLlama, said the incident involved a company providing web performance tracking whose scripts were loaded by Polymarket.
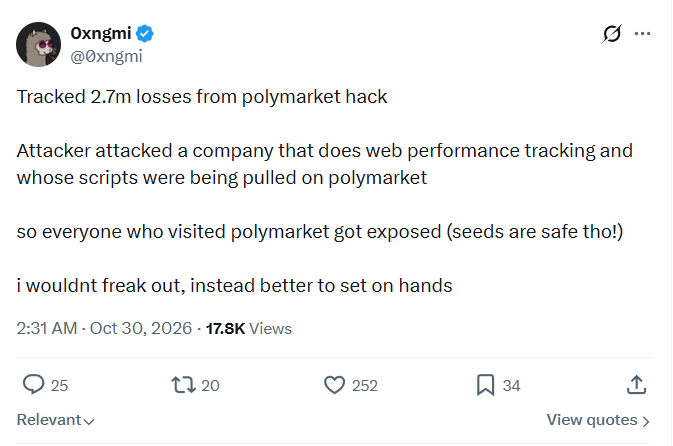
“Attacker attacked a company that does web performance tracking and whose scripts were being pulled on Polymarket, so everyone who visited polymarket got exposed,” 0xngmi wrote, adding that users’ wallet seed phrases remained safe.
Arkham traces suspected attacker funds
Arkham data identified a wallet believed to belong to a suspected attacker holding about $2.65 million in POL. The wallet showed multiple recent swaps from USDC.e into POL through Relay before funds were later moved to different addresses.
Separately, 0xngmi said roughly $2.7 million in losses had been tracked in connection with the exploit. The figures describe different observations: Arkham tracked the value held by a suspected attacker wallet, while 0xngmi estimated losses attributed to the incident.
Earlier Polymarket security incidents
Polymarket also suffered a security breach in May that resulted in approximately $700,000 in cryptocurrency being stolen after hackers compromised a six-year-old private key used for internal operations. Bubblemaps reported that attackers transferred POL across 16 addresses, including addresses associated with cryptocurrency exchanges.
Polymarket said customer funds, smart contracts and market resolution systems were unaffected by that earlier incident. The company rotated the compromised key, revoked production permissions and said it planned to migrate its private keys to a more secure key management system.
Other earlier issues included an alleged governance attack last year involving a market on whether Ukraine would agree to President Trump’s mineral deal by a specified date. Suspicious outflows tied to Polymarket’s UMA CTF Adapter infrastructure on Polygon also prompted an internal investigation earlier this year.
This article has been refined and enhanced by ChatGPT.


