



 USD

Google Tests MPC Crypto Custody System as Key Security Risks Mount

Alphabet Uses Service on Ethereum and Solana Ahead of Commercial Rollout
TL;DR
- Google Multi-Party Compute is in private preview, with major financial institutions testing the crypto custody security service.
- Alphabet is already using the technology to secure digital assets on Ethereum and Solana.
- The rollout comes as private-key theft remains a major security problem.
Trade smarter on Jupiter, Solana’s leading DEX built for fast execution and deep liquidity.
Swap tokens at competitive rates, route across multiple liquidity sources automatically, and access perpetuals, DCA, and advanced trading tools — all in one place!
Google is preparing to showcase Google Multi-Party Compute, a security service designed to help banks and other financial institutions safeguard and transfer cryptocurrencies and tokenized assets. The product remains in private preview, with several design partners and major financial institutions testing it, while parent company Alphabet has begun using the technology for its own digital assets on Ethereum and Solana. Commercial availability is planned for early 2027.
The company plans to present the system at its inaugural digital assets symposium in New York City. Google has not identified the institutions testing the product, the specific digital assets Alphabet is securing or the pricing planned for the commercial service. The offering marks Google’s first dedicated MPC custody product for cryptocurrencies, building on Google Cloud Key Management Service and Cloud HSM, which already help institutions manage cryptographic keys. Google previously published guidance in 2023 on building MPC-based digital-asset systems with its Confidential Space infrastructure.
“Digital asset adoption and tokenization are at an inflection point. As regulated financial institutions begin adopting blockchains and tokenization, they need scalable, proven infrastructure to secure their clients’ assets,” said Rich Widmann, director of digital assets strategy at Google Cloud.
How Google MPC Splits Control of Crypto Keys
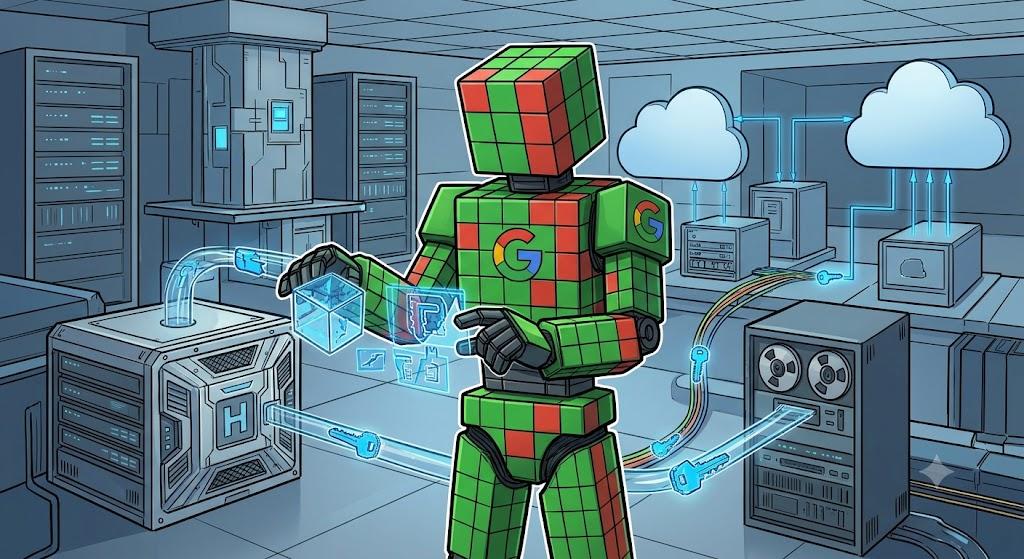
Multi-party computation, or MPC, avoids keeping a complete private key in one location. Instead, cryptographic information needed to authorize a transaction is divided among separate participants or computing environments. The pieces work together when a transaction is signed, reducing dependence on any single machine or holder of a full private key.
Google said customers retain control of their key material and that the company cannot access it in unencrypted form, including when key shares are stored on Google infrastructure. The system combines MPC-based signing with transaction policies and key recovery rather than requiring institutions to assemble those functions independently.
A bank could, for example, distribute signing credentials across Google Cloud, its own hardware and another cloud provider. When a transaction is initiated, Google’s Confidential Space can run a policy engine before signing begins. Institutional rules could impose transfer limits, restrict destination wallets or require approval from several departments. Confidential Space uses hardware-isolated computing environments intended to protect sensitive information from unauthorized access.
Google said institutions can also select different signing thresholds. A transaction might require two of three participating signers or five of seven to jointly produce a valid signature. Credentials can be spread across an institution’s own systems, Google Cloud and competing cloud infrastructure, limiting reliance on a single provider for control of the assets. Google also said the service supports fast transaction signing and key recovery.
That architecture does not remove every custody risk. Transaction security still depends on how an institution configures its system, protects participants and controls access to approval policies. Legitimate users can also still be deceived into approving malicious transfers, even when the underlying signing credentials have not been directly compromised.
Private-Key Compromises Drive Billions in Crypto Losses
Private-key theft remains a significant source of cryptocurrency losses. An attacker who obtains the credentials controlling a wallet may be able to move its assets without the owner’s authorization, making key management central to institutional crypto custody.
The available figures show the scale of that exposure:
Chainalysis and DeFiLlama data place private-key compromises among the major drivers of crypto theft, while the Resolv and Humanity Protocol incidents show how compromised credentials can affect both directly held assets and wider project operations.
Google Positions MPC Against AI and Future Quantum Risks
Google is also presenting the service against a wider cybersecurity backdrop that includes artificial intelligence and, over the longer term, quantum computing. The current MPC system is focused on existing threats such as compromised credentials and unauthorized transactions rather than an AI system breaking the cryptographic signatures protecting major blockchains.
Chainalysis found that cryptocurrency scams linked to AI-tool vendors extracted an average of $3.2 million per operation in 2025, compared with $719,000 for scams without such links, or roughly 4.5 times as much. The findings suggested AI could be helping fraudsters operate at greater scale but did not establish that AI directly caused the higher proceeds.
Ethereum researcher Justin Drake has warned that advances in AI could eventually uncover mathematical shortcuts affecting the signatures protecting Bitcoin and Ethereum wallets, with a worst-case breakthrough potentially emerging within months rather than years. No AI system has demonstrated the ability to break those signatures.
Quantum computing presents a different, longer-term issue. Google researchers have estimated that a sufficiently powerful future quantum computer could theoretically derive a bitcoin private key from an exposed public key in roughly 9 minutes with advanced preparation. About 6.9 million bitcoin have been reported as potentially vulnerable to future quantum attacks because their public keys have already been exposed, although no existing quantum computer can perform such an attack.
Google said the MPC architecture is designed to support future post-quantum cryptography upgrades as blockchain networks adopt the required technology. At general availability, the service is designed to support conventional ECDSA and Ed25519 signing algorithms. Google said future cryptographic upgrades could be added without requiring institutions to redesign their systems or interrupt operations.
Google Moves Toward a Crowded Institutional Custody Market
Google’s planned service would put one of the world’s largest cloud providers closer to specialist crypto security companies including Fireblocks, Fordefi and BitGo, which already provide technology for protecting and authorizing blockchain transactions.
Google argues that its existing banking relationships and security infrastructure can give it an advantage while allowing financial institutions to operate their own custody businesses. The company is positioning itself as an infrastructure provider rather than requiring institutions to hand complete control of signing credentials to one technology vendor.
That model still leaves institutions dependent on Google for parts of the software, transaction policies and operational infrastructure. Security will therefore depend on how customers distribute credentials, configure signing participants and control changes to transaction-approval policies as the service moves from private testing toward commercial deployment.
This article has been refined and enhanced by ChatGPT.


