



 USD

Coinbase Denies Hack as Bithumb Confirms Separate Employee-System Breach

Customer information was exposed across distinct incidents affecting exchanges and Korean financial firms
TL;DR
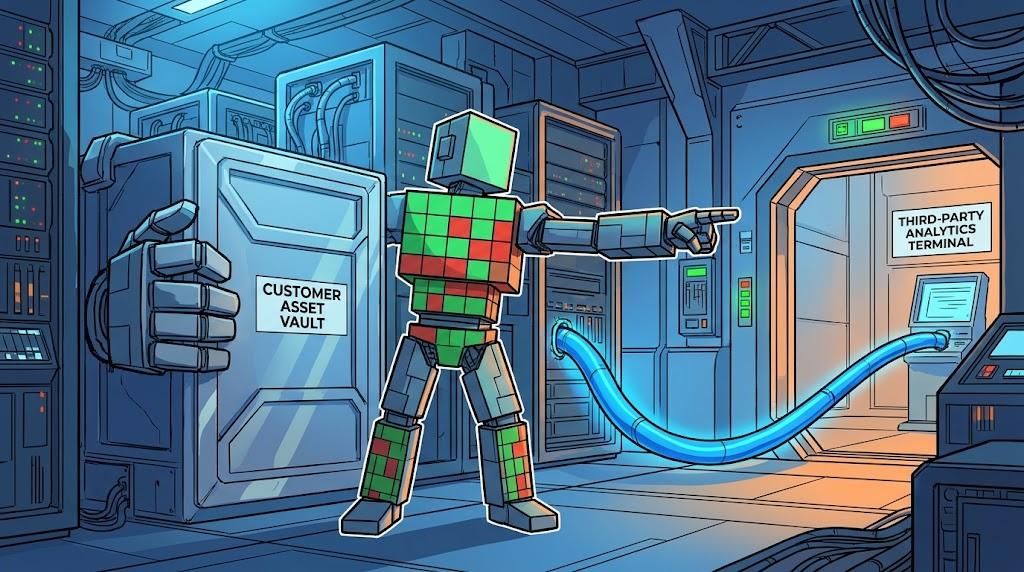
- Coinbase said its own systems were not hacked and traced customer-data exposure to third-party analytics provider Amplitude.
- Bithumb said an outsider breached an internal employee system, while its trading platform and customer virtual assets remained separate.
- South Korean regulators were also assessing cybersecurity incidents involving Daishin Securities and Mirae Asset Global Investments.
Trade smarter on Jupiter, Solana’s leading DEX built for fast execution and deep liquidity.
Swap tokens at competitive rates, route across multiple liquidity sources automatically, and access perpetuals, DCA, and advanced trading tools — all in one place!
Coinbase denied reports that it had been hacked, saying customer funds remain safe and the customer-data exposure originated at Amplitude, a third-party analytics provider. Separately, Bithumb said an outsider broke into the internal mobile system used by employees for work and messaging and took personal information. Bithumb said the employee system operates separately from its trading platform, and no crypto funds had been reported lost as of Asian afternoon hours.
Coinbase Traces Data Exposure to Amplitude
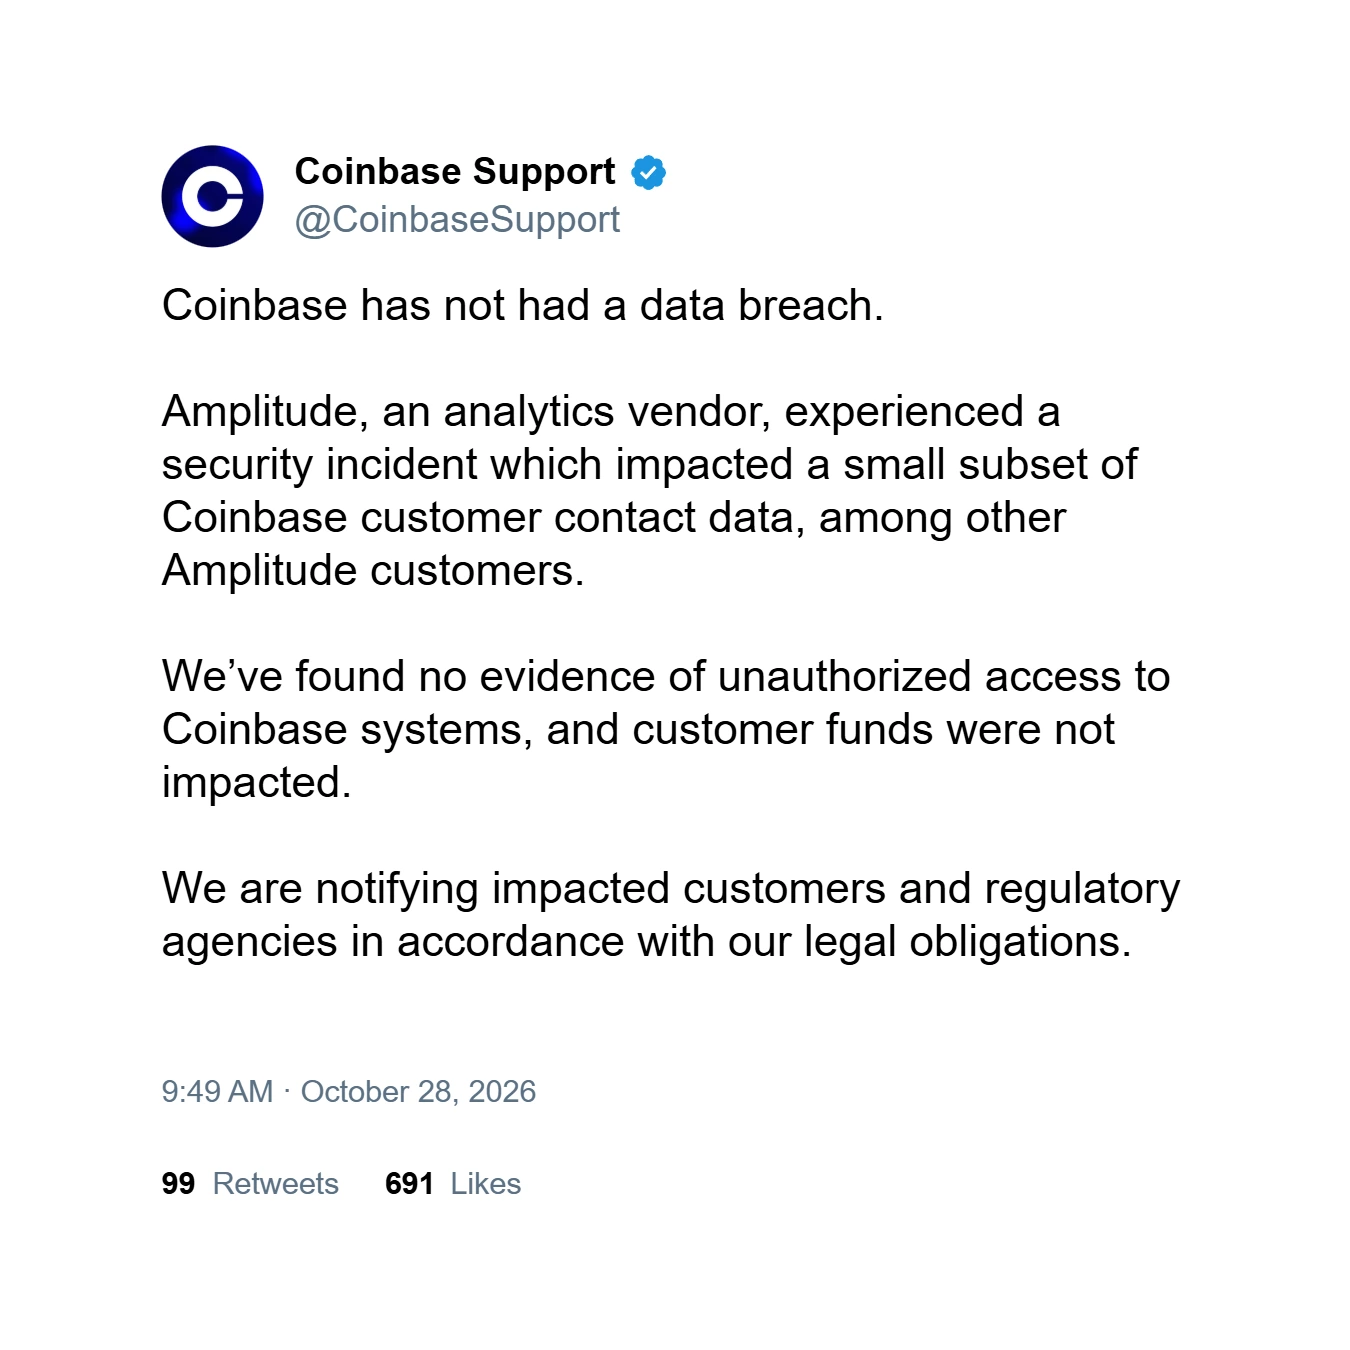
Nasdaq-listed Coinbase said the exposed information represented only a “small subset” of customer contact data and was compromised alongside information belonging to other Amplitude clients, according to Coinbase Support’s X account.
Coinbase said it was notifying affected customers by email as required by law and stressed that its systems had detected no unauthorized access. Customer funds, passwords and private keys were not compromised. Exposed email addresses or phone numbers can still be used in phishing or social-engineering attempts.
Coinbase had not specified how many customers were affected or exactly which contact-data fields were involved. The incident therefore centered on a third-party service used by the exchange rather than unauthorized access to Coinbase’s own infrastructure. That distinction separates the customer-data exposure from a direct compromise of the exchange’s systems, even though affected customers could still face attempts to misuse their contact information.
Bithumb Says Trading Platform Was Isolated From Breach
Bithumb, South Korea’s second-largest crypto exchange by trading volume, discovered its intrusion on Tuesday and reported it to the Korea Internet & Security Agency and the Personal Information Protection Commission. Bithumb told Yonhap it was analyzing the exact scope, “including the possibility of member information being involved.”
The exchange said the compromised employee system was isolated from its trading infrastructure, adding that “customer virtual assets cannot be accessed through this breach.” It had not said whether deposits or withdrawals were affected or how many people’s data was exposed.
The incident came as South Korean authorities examined cyberattacks affecting multiple financial companies. The Financial Supervisory Service said Bithumb was among three firms being assessed on Wednesday. The cases involved different systems and reported outcomes.
Financial Supervisory Service Governor Lee Chan-jin told a meeting with bank holding company chairs, “I understand that major financial investment companies experienced overall hacking incidents yesterday.” Earlier in the month, Lee said cyberattacks had affected 16 South Korean financial firms as of Oct. 14.
Bithumb’s latest incident followed an earlier internal-control failure in February. The exchange mistakenly credited customers with 620,000 BTC, worth more than $40 billion at the time, instead of 620,000 won. CEO Lee Jae-won blamed weak internal controls and said Bithumb was “acutely aware of the deficiency in internal system control.”
This article has been refined and enhanced by ChatGPT.


